Hackers Exploit VPN Flaw to Breach Japan's Digital Agency and Access 240,000 People's Data
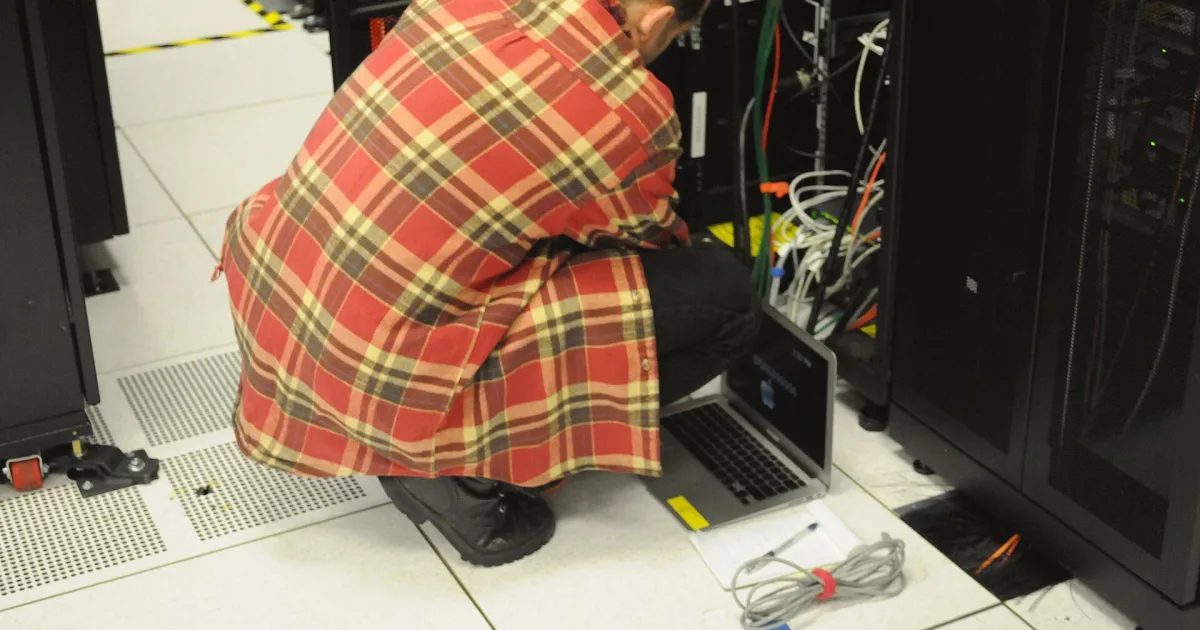
The personal information of about 240,000 government workers and contractors may have been exposed in an attack targeting a core network system, Japan's Digital Agency said on September 11.
The breach involved the Government Solution Service (GSS), the shared IT platform the agency provides to government ministries and agencies. Potentially exposed data includes names, email addresses, phone numbers and addresses.
According to the agency, the attackers compromised over 246,000 records containing names, approximately 236,000, addresses, around 1,000, email addresses, some 231,000, and phone numbers, roughly 94,000. The compromised information belongs to users, public officials, administrative staff, and businesses and individuals working with the service.
"We take this extremely seriously," Digital Agency Minister Hisashi Matsumoto told a news conference. "We will work to further strengthen security measures and do everything possible to prevent a recurrence."
## How the Intrusion Unfolded
The investigation found that a third party had infiltrated the system from around late May by exploiting a vulnerability in VPN equipment used to access the internal network. In July, the investigation determined that a flaw in a VPN product had been exploited to reach the system.
The agency opened its investigation in June after detecting access to a large number of server files through an account used by a network maintenance operator. Japan's Digital Agency blocked external access to the affected server and suspended the employee account used in the attack immediately after confirming the exploitation.
While the agency did not name the exploited VPN product, it said it would strengthen vulnerability management, noting that the targeted vulnerability had already been publicly disclosed before the attack was confirmed.
## What Was and Was Not Taken
The potentially affected data includes 189,000 records linked to employees of ministries, agencies and independent administrative institutions, and 57,000 records tied to contractors and others involved in their operations. The agency did not disclose which ministries or agencies may have been affected.
Most of the addresses and phone numbers are associated with the individuals' workplaces, namely a government building or an office, the agency explained in an accompanying FAQ. My Number identification data, bank account information and pension numbers were not included, and individual identification numbers and financial account information were not affected.
No other systems were compromised in the attack, and no information belonging to the general public was compromised, the agency said. No misuse of the leaked data has been confirmed.
## A Flagship Digital Project Under Strain
Introduced in 2021, the network is used by about 154,000 people across 23 organizations, including the agriculture ministry and the Cabinet Office. It was designed to improve productivity, security and telework by providing a shared government IT environment, making the breach a pointed embarrassment for the machinery of Japan's digital transformation.
The Digital Agency itself was established in September 2021 to oversee government information systems and efforts to digitize administrative services. The incident hands the agency a fresh test of that mandate.
Security researchers have repeatedly cautioned that patching alone cannot stop credential theft or persistent access once internet-edge devices are compromised, the category the exploited VPN product belongs to. Such devices remain prime targets because they sit exposed to the internet and routinely hold privileged credentials that attackers can harvest for durable footholds.
The fact that the flaw exploited against the GSS had been publicly disclosed before the attack was confirmed underscores the persistent gap between a patch being available and it being applied across large organizations, a gap that government networks in Japan are certainly not alone in facing.
The agency has not said whether it considers the incident part of a broader campaign against Japanese government infrastructure, and it declined to attribute the intrusion to any specific actor. It has also not ruled out further expansion of the known impact as its investigation continues.
## Minister Faces Questions Over Response
The September 11 announcement followed a news conference at which Minister Matsumoto disclosed the unauthorized access and set out the agency's initial response. The timeline disclosed by the agency shows the intruder gained access from around late May, that the suspicious file activity was detected in June, and that the VPN vulnerability was confirmed as the entry point in July, a sequence spanning weeks between initial compromise and full confirmation.
The agency says it has suspended the maintenance operator's account and taken other measures. For now, the disclosure stands as one of the larger government data breaches in Japan's recent history, and a reminder that the VPN gateways protecting public sector networks worldwide remain among the most exploited entry points in cybersecurity.
The case is also likely to feed an ongoing debate in Tokyo over the pace of Japan's cybersecurity reforms, which have accelerated in recent years amid rising regional tensions and a series of intrusions targeting government and defence-related organizations, with the Digital Agency's own systems now added to the list of high-profile compromises.
Discussion
Recommended for you
More technology
Cybersecurity
Global Ransomware Attacks Hit Record 997 in August as Utilities Surge
9/16/2026
Cybersecurity
ICE to Purchase Robot Dogs From Boston Dynamics for Officer Safety
9/2/2026
Cybersecurity
Jaguar Land Rover Extends Production Pause Until Sept 24 After Cyberattack Steals Data
9/2/2026
Cybersecurity